
Identity theft protection is sold as an app. It is a set of boring moves. Freeze your credit at Equifax, Experian, and TransUnion. Put an IRS IP PIN on the tax account. Use a password manager and passkeys. Stop SMS as the only second factor. If a form on your WordPress site collects anything like a Social Security number, you are in the identity business whether you meant to be or not.
Paid monitoring SKUs will mail you after your data is in a dump. Sometimes that mail is useful. It is not a freeze. Identity theft protection that does not start with the bureaus is a newsletter.
On this page
Personal: freeze, PIN, passkeys
A credit freeze is free by US law. You create an account at each bureau and freeze. Lenders cannot open new credit in your name until you thaw, which you can do for a window. That is the highest-leverage identity theft protection you can finish this morning. Paid “lock” buttons inside a bureau’s upsell are not the same as a freeze. Freeze.
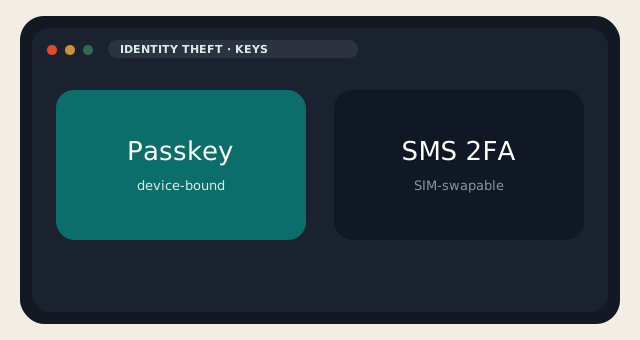
Have I Been Pwned for email. Unique passwords. Passkeys or TOTP on email, banks, Apple, Google, the registrar, and the host. SMS 2FA is better than nothing and worse than a SIM-swap. If your number is the account, a carrier desk is the attacker’s helpdesk. Registrar locks and a domain PIN belong here too — losing the domain is how a site becomes someone else’s phishing kit.
- Freeze Equifax, Experian, TransUnion. ChexSystems if you want the bank-account version.
- IRS IP PIN at irs.gov so a tax return in your SSN has to know the PIN.
- Password manager. Passkeys on the important desks.
- Skip SMS as the only factor. Authenticator app or hardware key.
- FTC IdentityTheft.gov if you are already in the incident, not as a screensaver.
VPN ads will try to sit in this article. A VPN is not identity theft protection. It is a tunnel. Useful on bad Wi-Fi. Irrelevant to a bureau freeze. Same for “AI dark web scans” that reprint Have I Been Pwned with a logo.
If you run a site that holds anyone’s data
Identity theft protection for a host is: collect less, store less, HTTPS everywhere, updates, 2FA on wp-admin, no PHP in uploads, backups that are not sitting next to the web root. Our WordPress hosting floor is LiteSpeed plus Imunify plus WP Toolkit. You still should not put SSNs in a $5 form plugin. If you must, you wanted a real processor and a lawyer, not a gist from an agent.
Access logs, admin users you can name, and a plugin list you can defend are part of identity theft protection. So is not emailing CSVs of customers to a personal Gmail. So is a registrar lock. So is not sharing the cPanel password in Slack. The WordPress hardening piece is the companion.
If you lease IPv4 or run mail, reputation is adjacent. A compromised site that sends is how a prefix gets a reputation you will feel. Freeze the account, rotate, restore. Check the path on an IP lookup when the mail already died.
When it already happened
| If this happened | Do this first | Then |
|---|---|---|
| New credit you did not open | Freeze all three (if not already); FTC report | Dispute at the bureaus, talk to the lender |
| Tax return rejected / filed | IRS IP PIN; IdentityTheft.gov | IRS identity-theft process, not a tweet |
| Email takeover | Recover, passkeys, session kill | Assume every reset mail is hostile |
| WordPress admin you did not create | Snapshot; rotate; restore known-good | Do not “clean” live without a copy |
| SIM swap | Carrier account PIN; move number if needed | Replace SMS 2FA everywhere |
Identity theft protection after the fact is slower than the freeze you skipped. Paid monitoring may catch a bureau inquiry. It will not un-file the tax return. Do the freezes even if you also buy a product. Especially if you buy a product.
None of this is legal advice. It is the checklist we give people who asked how identity theft protection works and expected a coupon. Freeze. Passkeys. Collect less. Restore. The rest is optional, and optional is how vendors eat a subscription.
Kids and elders: identity theft protection is often a family job. A parent’s email is the recovery account for three children. An elder’s landline is still an SMS target. Freeze their bureaus too. Put the PINs in the same manager you already made them use. Do not print the PINs on a sticky note on the router.
Mail is a vector. A compromised mailbox is how every reset flows. If you host mail on cPanel, 2FA the panel, rotate the mailbox password, and do not forward everything to a Gmail you share. Identity theft protection without mailbox hygiene is a freeze with a hole. Same for the domain registrar: lock, PIN, unique email.
Public records and data brokers are the slow leak. Opt-out is miserable and still worth a Saturday if you are a likely target — journalists, execs, anyone who has been doxxed once. That is identity theft protection as chores, not as a product. A vendor who promises to “remove you from 200 sites” is selling a queue, not a guarantee.
If you run WordPress for other people, tell them this page exists and then do the origin work: HTTPS, updates, 2FA, less PII. Identity theft protection is a partnership between the human who freezes the bureaus and the host who does not leak the form. We can be the second half. The freeze is still theirs.
Do the three freezes this week. That is the whole identity theft protection sermon. Passkeys after. Plugin updates after that. A monitoring SKU last, if ever. Anything that reverses that order is selling you a letter.
Reader discussion
Join the conversation.
Questions, corrections, and useful context are welcome.